Cybersecurity Archives - gettectonic.com - Page 3
AI Strategy for Your Business

AI Strategy for Your Business

How to Create a Winning AI Strategy for Your Business To maximize the value of AI, organizations must align their AI projects with strategic business objectives. Here’s a 10-step guide to crafting an effective AI strategy, including sample templates to support your planning. While AI adoption is on the rise, many companies still struggle to unlock its full potential. According to the 2024 IDC report Scaling AI Initiatives Responsibly, even organizations with advanced AI practices, termed “AI Masters,” face a 13% failure rate, while those still emerging in AI see a 20% failure rate. Challenges such as poor data quality and cultural resistance often contribute to these failures. To avoid these pitfalls, companies need to adopt a more deliberate and strategic approach to AI implementation. As Nick Kramer from SSA & Company states, “It’s not just about implementing the right technology; a lot of work needs to be done beforehand to succeed with AI.” What is an AI Strategy and Why is it Important? An AI strategy unifies all necessary components—such as data, technology, and talent—required to achieve business goals through AI. This includes: A well-designed AI strategy sets clear directions on how AI should be leveraged to achieve optimal outcomes within the organization. 10 Steps to Craft a Successful AI Strategy Resources for AI Strategy Templates If you’re ready to start building your AI strategy, here are several resources offering templates and guidance: By following these steps and utilizing the right resources, businesses can ensure they capture AI in ways that align with their strategic goals and maximize their competitive edge. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
Veeam Latest Acquisition

Veeam Latest Acquisition

Veeam continues its acquisition strategy with the purchase of Alcion, bolstering its capabilities in AI and as-a-service offerings. This acquisition follows Veeam’s investment in Microsoft 365 backup-as-a-service provider Alcion last year, and brings in a team of AI and security specialists. Analysts and Veeam executives see this move as a key step in expanding Veeam’s as-a-service offerings. Earlier this year, the company launched Veeam Data Cloud, a backup-as-a-service solution for Microsoft 365 and Azure workloads. “After years of resisting, Veeam has fully embraced the as-a-service model,” said Christophe Bertrand, an analyst at TheCube Research. Veeam Latest Acquisition The acquisition, which closed in mid-September, marks the second time Veeam has purchased a company founded by Niraj Tolia and Vaibhav Kamra. In 2020, Veeam acquired Kasten, their Kubernetes backup provider. A year ago, Veeam led a million funding round for Alcion, which has since developed AI-driven data protection solutions. Veeam has been active in acquisitions, joining a broader trend in the data protection market. Recently, Commvault acquired Clumio, Cohesity merged with Veritas, and Veeam itself bought Cirrus from CT4, which later became part of the Veeam Data Cloud. Earlier this year, Veeam also acquired Coveware, an incident response vendor. “Veeam hasn’t traditionally been an acquisition-heavy company, but that has changed in recent years,” said Rick Vanover, Veeam’s VP of product strategy. “I expect this trend to continue.” Alcion’s Role at Veeam This acquisition strengthens Veeam’s expertise in the fast-growing as-a-service market. Alcion’s team of fewer than 50 employees, including founders Niraj Tolia and Vaibhav Kamra, joins Veeam, with Tolia stepping in as Veeam’s new CTO. Tolia will lead product strategy and engineering for Veeam Data Cloud, succeeding Danny Allan, who recently became CTO at cybersecurity company Snyk. Alcion, which has hundreds of customers, will offer those customers the opportunity to transition to Veeam Data Cloud. However, Veeam has not finalized the future of Alcion’s product or established a timeline for its integration. “This acquisition brings incredible talent and thought leadership to Veeam, especially from Niraj and the Alcion team,” said Brandt Urban, Veeam’s senior VP of worldwide cloud sales. “Their expertise will help us rapidly enhance Veeam Data Cloud, adding more capabilities and expanding workload coverage.” Analysts, like Bertrand, expect Veeam to broaden its data protection offerings for additional SaaS platforms beyond Microsoft 365, looking toward collaboration and DevOps tools as potential areas for growth. AI and Security at the Forefront Alcion’s AI-powered features allow administrators to optimize backups, detect malware, and respond proactively to threats. According to Krista Case, an analyst at The Futurum Group, Alcion uses AI strategically to adapt backup schedules based on data modification patterns, trigger backups when potential threats are identified, and recommend the best recovery points. “When practitioners talk about cyber resilience, they’re focused on minimizing data loss and downtime—Alcion’s AI capabilities directly address these concerns,” said Case. Veeam has also been integrating AI into its existing products, offering inline malware detection and an Intelligent Diagnostics service. A forthcoming Copilot feature for Microsoft 365 backups will further enhance AI-driven data protection. Veeam Latest Acquisition “AI is a real asset when applied thoughtfully—it’s not just hype,” said Bertrand, adding that users are more interested in AI’s ability to drive outcomes, like detecting threats that could otherwise go unnoticed. Veeam executives echoed the importance of delivering clear, tangible AI benefits. “We keep user outcomes front and center because, otherwise, AI becomes an expensive experiment,” Vanover said. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
AI Revolution in Government

AI Revolution in Government

The AI Revolution in Government: Unlocking Efficiency and Public Trust As the AI boom accelerates, it’s essential to explore how artificial intelligence can streamline operations for government and public sector organizations. From enhancing data processing to bolstering cybersecurity and improving public planning, AI has the potential to make government services more efficient and effective for both agencies and constituents. AI Revolution in Government. The Role of AI in Public Sector Efficiency AI presents significant opportunities for government agencies to optimize their operations. By integrating AI-driven tools, public agencies can improve service delivery, boost efficiency, and foster greater trust between the public and private sectors. However, with these advancements comes the challenge of bridging the AI skills gap — a pressing concern as organizations ramp up investments in AI without enough trained professionals to support its deployment. According to a survey by SAS, 63% of decision-makers across various sectors, including government, believe they lack the AI and machine learning resources necessary to keep pace with the growing demand. This skills gap, combined with rapid AI adoption, has many workers concerned about the future of their jobs. Predictions from Goldman Sachs suggest that AI could replace 300 million full-time jobs globally, affecting nearly one-fifth of the workforce, particularly in fields traditionally considered automation-proof, such as administrative and legal professions. Despite concerns about job displacement, AI is also expected to create new roles. The World Economic Forum’s Future of Jobs Report estimates that 75% of companies plan to adopt AI, with 50% anticipating job growth. This presents a crucial opportunity for government organizations to upskill their workforce and ensure they are prepared for the changes AI will bring. Preparing for an AI-Driven Future in Government To fully harness the benefits of AI, public sector organizations must first modernize their data infrastructure. Data modernization is a key step in setting up a future-ready organization, allowing AI to operate effectively by leveraging accurate, connected, and real-time data. As AI automates lower-level tasks, government workers need to transition into more strategic roles, making it essential to invest in AI training and upskilling programs. AI Applications in GovernmentAI is already transforming various government functions, improving operations, and meeting the needs of citizens more effectively. The possibilities are vast: While AI holds immense potential, its successful adoption depends on having a digital-ready workforce capable of managing these applications. Yet, many government employees lack the data science and AI expertise needed to manage large citizen data sets and develop AI models that can improve service delivery. Upskilling the Government Workforce for AI Investing in AI education is critical to ensuring that government employees can meet the demands of the future. Countries like Finland and Singapore have already launched national AI training programs to prepare their populations for the AI-driven economy. For example, Finland’s “Elements of AI” program introduced AI basics to the public and has been completed by over a million people worldwide. Similarly, AI Singapore’s “AI for Everyone” initiative equips individuals and organizations with AI skills for social good. In the U.S., legislation is being considered to create an AI training program for federal supervisors and management officials, helping government leaders navigate the risks and benefits of AI in alignment with agency missions. The Importance of Trust and Data Security As public sector organizations embrace AI, trust is a critical factor. AI tools are only as effective as the data they rely on, and ensuring data integrity, security, and ethical use is paramount. The rise of the Chief Data Officer highlights the growing importance of managing and protecting government data. These roles not only oversee data management but also ensure that AI technologies are used responsibly, maintaining public trust and safeguarding privacy. By modernizing data systems and equipping employees with AI skills, government organizations can unlock the full potential of AI and automation. This transformation will help agencies better serve their communities, enhance efficiency, and build lasting trust with the people they serve. The Future of AI in Government The future of AI in government is bright, but organizations must take proactive steps to prepare for it. By unifying and securing their data, investing in AI training, and focusing on ethical AI deployment, public sector agencies can harness AI’s power to drive meaningful change. Ultimately, this is an opportunity for the public sector to improve service delivery, support their workforce, and build stronger connections with citizens. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More

Challenges of EHR Implementation in Healthcare

Challenges of EHR Implementation and How to Overcome Them Implementing an electronic health record (EHR) system is a monumental task, with complexities that require careful planning and execution. Common challenges—such as resistance to change, data migration hurdles, cost overruns, cybersecurity risks, and patient engagement issues—can impede progress. However, understanding these obstacles and applying targeted strategies can pave the way for a smooth transition. 1. Resistance to Change The adoption of a new EHR system affects nearly every workflow in a healthcare organization, often sparking resistance among staff. Fear of change and attachment to familiar processes can hinder implementation. Solution: 2. Data Migration Issues Accurate migration of patient health records is critical, yet transitioning data between systems often presents technical and logistical challenges. Solution: 3. Cost Overruns EHR implementation costs can quickly escalate, extending beyond software and hardware expenses to include consulting fees, training, and operational adjustments. Solution: 4. Heightened Cybersecurity Risks Transitioning sensitive patient data between EHR systems increases vulnerability to breaches, ransomware, and other cybersecurity threats. Solution: 5. Patient Engagement Challenges Patients are often overlooked during EHR transitions, leading to confusion about changes in medication requests, appointment scheduling, and other interactions. Solution: Conclusion EHR implementation is undoubtedly challenging, but with proactive strategies, healthcare organizations can navigate these complexities effectively. By addressing resistance to change, ensuring seamless data migration, managing costs, bolstering cybersecurity, and engaging patients, organizations can achieve a successful EHR transition that enhances workflows, safeguards data, and improves patient outcomes. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Marketing Cloud Transactional Emails Salesforce Marketing Cloud Transactional Emails are immediate, automated, non-promotional messages crucial to business operations and customer satisfaction, such as order Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more

Read More
New Technology Risks

New Technology Risks

Organizations have always needed to manage the risks that come with adopting new technologies, and implementing artificial intelligence (AI) is no different. Many of the risks associated with AI are similar to those encountered with any new technology: poor alignment with business goals, insufficient skills to support the initiatives, and a lack of organizational buy-in. To address these challenges, executives should rely on best practices that have guided the successful adoption of other technologies, according to management consultants and AI experts. When it comes to AI, this includes: However, AI presents unique risks that executives must recognize and address proactively. Below are 15 areas of risk that organizations may encounter as they implement and use AI technologies: Managing AI Risks While the risks associated with AI cannot be entirely eliminated, they can be managed. Organizations must first recognize and understand these risks and then implement policies to mitigate them. This includes ensuring high-quality data for AI training, testing for biases, and continuous monitoring of AI systems to catch unintended consequences. Ethical frameworks are also crucial to ensure AI systems produce fair, transparent, and unbiased results. Involving the board and C-suite in AI governance is essential, as managing AI risk is not just an IT issue but a broader organizational challenge. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Marketing Cloud Transactional Emails Salesforce Marketing Cloud Transactional Emails are immediate, automated, non-promotional messages crucial to business operations and customer satisfaction, such as order Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more

Read More
CISA Launches New Services Portal

CISA Launches New Services Portal

CISA Launches New Services Portal to Enhance Incident Reporting and Support In August, the Cybersecurity and Infrastructure Security Agency (CISA) introduced the CISA Services Portal, designed to streamline the process of reporting cybersecurity incidents and enhance information sharing. “The new CISA Services Portal improves the reporting process and offers more features for our voluntary reporters. We ask organizations reporting an incident to provide details such as the impacted entity, contact information, incident description, technical indicators, and mitigation steps,” a CISA spokesperson stated via email. By collecting detailed reports, CISA and its partners can assist victims in mitigating the effects of cyber incidents, prevent attackers from reusing tactics, and gain insights into the broader scope of adversary campaigns. This information-sharing benefits not just the initial victim but also helps protect other organizations from potential attacks. How the Portal Works The CISA Services Portal follows guidelines outlined in the NIST Special Publication 800-61 Revision 2, which defines a cyber incident as: In addition to cyber incidents, users can report malware, software vulnerabilities, threat indicators, and vulnerabilities in government websites. For reporting cyberattacks on critical infrastructure, users are directed to a different link as required by CIRCIA regulations. When using the portal, users are guided through a step-by-step reporting process, which includes identifying the affected organization, providing a detailed description of the incident, and outlining the technical details of the breach. What Makes CISA’s Portal Unique? While many breach reporting portals exist, CISA’s stands out for several reasons. It is a voluntary, stand-alone government portal available to all entities nationwide. It does not replace any breach reporting processes mandated by federal, state, local, or industry-specific regulations, such as those required by the FTC or FCC. The portal allows users to report incidents on behalf of their organization or as individual users. It also offers the option to set up an account for ongoing communication with CISA, where users can save, update, and share reports. What truly differentiates CISA’s portal is its capability to provide direct assistance in incident response and recovery. This is particularly valuable for small and medium-sized businesses that may lack the resources to effectively handle cyber incidents. Although reporting to CISA is not mandatory, the agency strongly encourages organizations to voluntarily report incidents or suspicious activity. CISA has also developed a guide to help prepare organizations for submitting reports, ensuring they have all necessary details related to the breach and their mitigation efforts. “Any organization experiencing a cyberattack or incident should report it—not only for their benefit but to help the broader community. CISA and our government partners have unique tools to assist with response and recovery, but we need to know about the incident to provide support,” said Jeff Greene, CISA Executive Assistant Director for Cybersecurity, in a statement announcing the portal. The new CISA Services Portal aims to strengthen collaboration, offering a more efficient and supportive environment for incident reporting and response. Salesforce comment: SAN FRANCISCO, Sept. 25, 2015—Salesforce (NYSE: CRM), the Customer Success Platform and world’s #1 CRM company, today issued the following statement on the proposed Cybersecurity Information Sharing Act of 2015 (“CISA”): “At Salesforce, trust is our number one value and nothing is more important to our company than the privacy of our customers’ data,” said Burke Norton, chief legal officer, Salesforce. “Contrary to reports, Salesforce does not support CISA and has never supported CISA.” Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
Open AI Update

Open AI Update

OpenAI has established itself as a leading force in the generative AI space, with its ChatGPT being one of the most widely recognized AI tools. Powered by the GPT series of large language models (LLMs), as of September 2024, ChatGPT primarily uses GPT-4o and GPT-3.5. This insight provides an Open AI Update. In August and September 2024, rumors circulated about a new model from OpenAI, codenamed “Strawberry.” Initially, it was unclear if this model would be a successor to GPT-4o or something entirely different. On September 12, 2024, the mystery was resolved with the official launch of OpenAI’s o1 models, including o1-preview and o1-mini. What is OpenAI o1? OpenAI o1 is a new family of LLMs optimized for advanced reasoning tasks. Unlike earlier models, o1 is designed to improve problem-solving by reasoning through queries rather than just generating quick responses. This deeper processing aims to produce more accurate answers to complex questions, particularly in fields like STEM (science, technology, engineering, and mathematics). The o1 models, currently available in preview form, are intended to provide a new type of LLM experience beyond what GPT-4o offers. Like all OpenAI LLMs, the o1 series is built on transformer architecture and can be used for tasks such as content summarization, new content generation, question answering, and writing code. Key Features of OpenAI o1 The standout feature of the o1 models is their ability to engage in multistep reasoning. By adopting a “chain-of-thought” approach, o1 models break down complex problems and reason through them iteratively. This makes them particularly adept at handling intricate queries that require a more thoughtful response. The initial September 2024 launch included two models: Use Cases for OpenAI o1 The o1 models can perform many of the same functions as GPT-4o, such as answering questions, summarizing content, and generating text. However, they are particularly suited for tasks that benefit from enhanced reasoning, including: Availability and Access The o1-preview and o1-mini models are available to users of ChatGPT Plus and Team as of September 12, 2024. OpenAI plans to extend access to ChatGPT Enterprise and Education users starting September 19, 2024. While free ChatGPT users do not have access to these models at launch, OpenAI intends to introduce o1-mini to free users in the future. Developers can also access the models through OpenAI’s API, and third-party platforms such as Microsoft Azure AI Studio and GitHub Models offer integration. Limitations of OpenAI o1 As preview models, o1 comes with certain limitations: Enhancing Safety with OpenAI o1 To ensure safety, OpenAI released a System Card that outlines how the o1 models were evaluated for risks like cybersecurity threats, persuasion, and model autonomy. The o1 models improve safety through: GPT-4o vs. OpenAI o1 Here’s a quick comparison between GPT-4o and OpenAI’s new o1 models: Feature GPT-4o o1 Models Release Date May 13, 2024 Sept. 12, 2024 Model Variants Single model Two variants: o1-preview and o1-mini Reasoning Capabilities Good Enhanced, especially for STEM fields Mathematics Olympiad Score 13% 83% Context Window 128K tokens 128K tokens Speed Faster Slower due to in-depth reasoning Cost (per million tokens) Input: $5; Output: $15 o1-preview: $15 input, $60 output; o1-mini: $3 input, $12 output Safety and Alignment Standard Enhanced safety, better jailbreak resistance OpenAI’s o1 models bring a new level of reasoning and accuracy, making them a promising advancement in generative AI. Like1 Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
chatGPT open ai 01

ChatGPT Open AI o1

OpenAI has firmly established itself as a leader in the generative AI space, with its ChatGPT being one of the most well-known applications of AI today. Powered by the GPT family of large language models (LLMs), ChatGPT’s primary models, as of September 2024, are GPT-4o and GPT-3.5. In August and September 2024, rumors surfaced about a new model from OpenAI, codenamed “Strawberry.” Speculation grew as to whether this was a successor to GPT-4o or something else entirely. The mystery was resolved on September 12, 2024, when OpenAI launched its new o1 models, including o1-preview and o1-mini. What Is OpenAI o1? The OpenAI o1 family is a series of large language models optimized for enhanced reasoning capabilities. Unlike GPT-4o, the o1 models are designed to offer a different type of user experience, focusing more on multistep reasoning and complex problem-solving. As with all OpenAI models, o1 is a transformer-based architecture that excels in tasks such as content summarization, content generation, coding, and answering questions. What sets o1 apart is its improved reasoning ability. Instead of prioritizing speed, the o1 models spend more time “thinking” about the best approach to solve a problem, making them better suited for complex queries. The o1 models use chain-of-thought prompting, reasoning step by step through a problem, and employ reinforcement learning techniques to enhance performance. Initial Launch On September 12, 2024, OpenAI introduced two versions of the o1 models: Key Capabilities of OpenAI o1 OpenAI o1 can handle a variety of tasks, but it is particularly well-suited for certain use cases due to its advanced reasoning functionality: How to Use OpenAI o1 There are several ways to access the o1 models: Limitations of OpenAI o1 As an early iteration, the o1 models have several limitations: How OpenAI o1 Enhances Safety OpenAI released a System Card alongside the o1 models, detailing the safety and risk assessments conducted during their development. This includes evaluations in areas like cybersecurity, persuasion, and model autonomy. The o1 models incorporate several key safety features: GPT-4o vs. OpenAI o1: A Comparison Here’s a side-by-side comparison of GPT-4o and OpenAI o1: Feature GPT-4o o1 Models Release Date May 13, 2024 Sept. 12, 2024 Model Variants Single Model Two: o1-preview and o1-mini Reasoning Capabilities Good Enhanced, especially in STEM fields Performance Benchmarks 13% on Math Olympiad 83% on Math Olympiad, PhD-level accuracy in STEM Multimodal Capabilities Text, images, audio, video Primarily text, with developing image capabilities Context Window 128K tokens 128K tokens Speed Fast Slower due to more reasoning processes Cost (per million tokens) Input: $5; Output: $15 o1-preview: $15 input, $60 output; o1-mini: $3 input, $12 output Availability Widely available Limited to specific users Features Includes web browsing, file uploads Lacks some features from GPT-4o, like web browsing Safety and Alignment Focus on safety Improved safety, better resistance to jailbreaking ChatGPT Open AI o1 OpenAI o1 marks a significant advancement in reasoning capabilities, setting a new standard for complex problem-solving with LLMs. With enhanced safety features and the ability to tackle intricate tasks, o1 models offer a distinct upgrade over their predecessors. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
Acceptable AI Use Policies

Acceptable AI Use Policies

With great power comes—when it comes to generative AI—significant security and compliance risks. Discover how AI acceptable use policies can safeguard your organization while leveraging this transformative technology. AI has become integral across various industries, driving digital operations and organizational infrastructure. However, its widespread adoption brings substantial risks, particularly concerning cybersecurity. A crucial aspect of managing these risks and ensuring the security of sensitive data is implementing an AI acceptable use policy. This policy defines how an organization handles AI risks and sets guidelines for AI system usage. Why an AI Acceptable Use Policy Matters Generative AI systems and large language models are potent tools capable of processing and analyzing data at unprecedented speeds. Yet, this power comes with risks. The same features that enhance AI efficiency can be misused for malicious purposes, such as generating phishing content, creating malware, producing deepfakes, or automating cyberattacks. An AI acceptable use policy is essential for several reasons: Crafting an Effective AI Acceptable Use Policy An AI acceptable use policy should be tailored to your organization’s needs and context. Here’s a general guide for creating one: Essential Elements of an AI Acceptable Use Policy A robust AI acceptable use policy should include: An AI acceptable use policy is not just a document but a dynamic framework guiding safe and responsible AI use within an organization. By developing and enforcing this policy, organizations can harness AI’s power while mitigating its risks to cybersecurity and data integrity, balancing innovation with risk management as AI continues to evolve and integrate into our digital landscapes. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
Challenges for Rural Healthcare Providers

Challenges for Rural Healthcare Providers

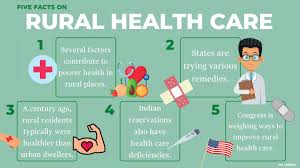
Rural healthcare providers have long grappled with challenges due to their geographic isolation and limited financial resources. The advent of digital health transformation, however, has introduced a new set of IT-related obstacles for these providers. EHR Adoption and New IT Challenges While federal legislation has successfully promoted Electronic Health Record (EHR) adoption across both rural and urban healthcare organizations, implementing an EHR system is only one component of a comprehensive health IT strategy. Rural healthcare facilities encounter numerous IT barriers, including inadequate infrastructure, interoperability issues, constrained resources, workforce shortages, and data security concerns. Limited Broadband Access Broadband connectivity is essential for leveraging health IT effectively. However, there is a significant disparity in broadband access between rural and urban areas. According to a Federal Communications Commission (FCC) report, approximately 96% of the U.S. population had access to broadband at the FCC’s minimum speed benchmark in 2019, compared to just 73.6% of rural Americans. The lack of broadband infrastructure hampers rural organizations’ ability to utilize IT features that enhance care delivery, such as electronic health information exchange (HIE) and virtual care. Rural facilities, in particular, rely heavily on HIE and telehealth to bridge gaps in their services. For instance, HIE facilitates data sharing between smaller ambulatory centers and larger academic medical centers, while telehealth allows rural clinicians to consult with specialists in urban centers. Additionally, telehealth can help patients in rural areas avoid long travel distances for care. However, without adequate broadband access, these services remain impractical. Despite persistent disparities, the rural-urban broadband gap has narrowed in recent years. Data from the FCC indicates that since 2016, the number of people in rural areas without access to 25/3 Mbps service has decreased by more than 46%. Various programs, including the FCC’s Rural Health Care Program and USDA funding initiatives, aim to expand broadband access in rural regions. Interoperability Challenges While HIE adoption is rising nationally, rural healthcare organizations lag behind their urban counterparts in terms of interoperability capabilities, as noted in a 2023 GAO report. Data from a 2021 American Hospital Association survey revealed that rural hospitals are less likely to engage in national or regional HIE networks compared to medium and large hospitals. Rural providers often lack the economic and technological resources to participate in electronic HIE networks, leading them to rely on manual data exchange methods such as fax or mail. Additionally, rural providers are less likely to join EHR vendor networks for data exchange, partly due to the fact that they often use different systems from those in other local settings, complicating health data exchange. Federal initiatives like TEFCA aim to improve interoperability through a network of networks approach, allowing organizations to connect to multiple HIEs through a single connection. However, TEFCA’s voluntary participation model and persistent barriers such as IT staffing shortages and broadband gaps still pose challenges for rural providers. Financial Constraints Rural hospitals often operate with slim profit margins due to lower patient volumes and higher rates of uninsured or underinsured patients. The financial strain is exacerbated by declining Medicare and Medicaid reimbursements. According to KFF, the median operating margin for rural hospitals was 1.5% in 2019, compared to 5.2% for other hospitals. With limited budgets, rural healthcare organizations struggle to invest in advanced health IT systems and the necessary training and maintenance. Many small rural hospitals are turning to cloud-based EHR platforms as a cost-effective solution. Cloud-based EHRs reduce the need for substantial upfront hardware investments and offer monthly subscription fees, some as low as $100 per month. Workforce Challenges The healthcare sector is facing widespread staff shortages, including a lack of skilled health IT professionals. Rural areas are disproportionately affected by these shortages. An insufficient number of IT specialists can impede the adoption and effective use of health IT in these regions. To address workforce gaps, the ONC suggests strategies such as cross-training multiple staff members in health IT functions and offering additional training opportunities. Some networks, like OCHIN, have secured grants to develop workforce programs, but limited broadband access can hinder participation in virtual training programs, highlighting the need for expanded broadband infrastructure. Data Security Concerns Healthcare data breaches have surged, with a 256% increase in large breaches reported to the Office for Civil Rights (OCR) over the past five years. Rural healthcare organizations, often operating with constrained budgets, may lack the resources and staff to implement robust data security measures, leaving them vulnerable to cyber threats. A cyberattack on a rural healthcare organization can disrupt patient care, as patients may need to travel significant distances to reach alternative facilities. To address cybersecurity challenges, recent legislative efforts like the Rural Hospital Cybersecurity Enhancement Act aim to develop comprehensive strategies for rural hospital cybersecurity and provide educational resources for staff training. In the interim, rural healthcare organizations can use free resources such as the Health Industry Cybersecurity Practices (HICP) publication to guide their cybersecurity strategies, including recommendations for managing vulnerabilities and protecting email systems. Does your practice need help meeting these challenges? Contact Tectonic today. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more Tectonic’s Successful Salesforce Track Record Salesforce Technology Services Integrator – Tectonic has successfully delivered Salesforce in a variety of industries including Public Sector, Hospitality, Manufacturing, Read more

Read More
Adopting Salesforce Security Policies

Adopting Salesforce Security Policies

Data breaches reached an all-time high in 2023, affecting more than 234 million individuals, and there’s no sign of the trend slowing down. At the center of this challenge is how organizations allocate resources to safeguard customer data. One of the most critical systems for managing this data is CRM platforms like Salesforce, used by over 150,000 U.S. businesses. However, security blind spots within Salesforce continue to pose significant risks. To address these concerns, the National Institute of Standards and Technology (NIST) offers a strategic framework for Salesforce security teams. In February 2024, NIST released Version 2.0 of its Cybersecurity Framework (CSF), marking the first major update in a decade. Key improvements include the introduction of a new “Govern” function, streamlining of categories to simplify usability, and updates to the “Respond” function to enhance incident management. This framework now applies across all industries, not just critical infrastructure. For Salesforce security leaders, these changes will significantly affect how they manage security, from aligning Salesforce practices with enterprise risk strategies to strengthening oversight of third-party apps. Here’s how these updates will influence Salesforce security going forward. What is the NIST Cybersecurity Framework 2.0? The NIST Cybersecurity Framework, first launched in 2014, was developed after an executive order by President Obama, aiming to provide a standardized set of guidelines to improve cybersecurity across critical infrastructure. The framework’s objectives include: The newly updated NIST CSF 2.0, released in 2024, expands on the original framework, providing organizations with structured, yet flexible, guidance for managing cybersecurity risks. It revolves around three core components: the CSF Core, CSF Profiles, and CSF Tiers. Key Components of NIST Cybersecurity Framework 2.0 These components help organizations understand, assess, and improve their cybersecurity posture, forming the basis for risk-informed strategies that align with organizational needs and the evolving threat landscape. Key Updates in the NIST Cybersecurity Framework 2.0 and Their Impact on Salesforce Security The 2024 updates to NIST CSF offer insights that Salesforce security leaders can use to align their strategies with evolving cybersecurity risks. Implementation Strategies for Salesforce Security Leaders To incorporate CSF 2.0 into Salesforce security operations, leaders should: Conclusion: Embracing NIST CSF 2.0 to Strengthen Salesforce Security The 2024 NIST Cybersecurity Framework updates offer crucial insights for Salesforce security leaders. By adopting these practices, organizations can enhance data protection, strengthen incident response capabilities, and ensure business continuity—critical for those relying on Salesforce for managing sensitive customer data. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Marketing Cloud Transactional Emails Salesforce Marketing Cloud Transactional Emails are immediate, automated, non-promotional messages crucial to business operations and customer satisfaction, such as order Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more

Read More
Iran-based cyber threat actors have been targeting U.S

Iran-based cyber threat actors have been targeting U.S

Iran-based cyber threat actors have been targeting U.S. and international organizations across various sectors, including healthcare, according to a joint cybersecurity advisory from the Cybersecurity and Infrastructure Security Agency (CISA), the FBI, and the Department of Defense Cyber Crime Center. The advisory highlights known threat groups such as Pioneer Kitten, UNC757, Parisite, Rubidium, and Lemon Sandstorm. These actors have been observed targeting a range of sectors including education, healthcare, defense, finance, and local government, as well as organizations in countries like Azerbaijan, the United Arab Emirates, and Israel. A significant portion of these actors’ operations against U.S. organizations involves gaining network access and subsequently collaborating with ransomware affiliates to deploy ransomware. The advisory notes that these actors offer full domain control and admin credentials to networks globally. Recently, they have been working directly with ransomware groups to facilitate encryption and share a percentage of ransom payments. The FBI has identified collaborations between these threat actors and ransomware affiliates such as NoEscape, Ransomhouse, and ALPHV. Despite their association with the Iranian government, these groups typically obscure their Iranian origins and provide vague details about their nationality when working with ransomware affiliates. Tracking of these Iranian cyber threat actors dates back to 2017, with recent activities documented up to August 2024. The advisory draws parallels with a September 2020 alert about Iran-backed hackers exploiting VPN vulnerabilities, based on previous FBI investigations. The advisory provides technical insights into the threat actors’ methods, including their use of public-facing network devices like Citrix Netscaler for initial access. To mitigate risks, the FBI and CISA recommend that organizations prioritize patching vulnerabilities associated with CVE-2024-3400, CVE-2022-1388, CVE-2019-19781, and CVE-2023-3519. Organizations are also advised to review security controls, examine logs, and search for unique identifiers and indicators of compromise. If organizations suspect they have been targeted by these Iranian cyber threat actors, they should contact their local FBI field office for assistance. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Marketing Cloud Transactional Emails Salesforce Marketing Cloud Transactional Emails are immediate, automated, non-promotional messages crucial to business operations and customer satisfaction, such as order Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more

Read More
Salesforce to Acquire Own

Salesforce to Acquire Own

Salesforce is set to acquire data protection and management vendor Own Co. for approximately $1.9 billion in cash. This move aligns with Salesforce’s ongoing investment in artificial intelligence (AI) and its efforts to bolster cybersecurity amidst rising data security concerns.  The San Francisco-based CRM giant expects to finalize the acquisition of Own by the fourth quarter of its fiscal year 2025, according to a company statement. Own, formerly known as OwnBackup, touts itself as the leading cloud data protection platform for Salesforce, serving around 7,000 customers with services such as data archiving, security, and analytics. He highlighted that Own’s expertise would enhance Salesforce’s data protection and management capabilities, reinforcing the company’s commitment to secure, end-to-end solutions. Sam Gutmann, CEO of Own, echoed the sentiment, stating that the acquisition would allow Own and Salesforce to drive innovation and secure data, particularly in highly regulated industries. Gutmann, who previously founded Intronis, has led Own’s growth since its establishment in 2015, with backing from investors like BlackRock and Salesforce Ventures. The acquisition is expected to strengthen Salesforce’s existing offerings, such as Backup, Shield, and Data Mask. Own, known for its data resilience platform, has raised over 0 million in funding and partnered with major tech players like ServiceNow and Microsoft Dynamics 365. The deal comes shortly after Salesforce announced plans to acquire Tenyx, an AI-powered voice agent startup, as part of its broader AI-driven strategy. Salesforce has shifted focus from larger acquisitions in recent years, prioritizing shareholder returns. However, this purchase reflects the company’s strategic shift towards enhancing its AI and data security solutions to maintain growth momentum. Salesforce anticipates that the Own deal will be accretive to free cash flow starting in the second year after the transaction closes, without affecting its current capital return program. This acquisition underscores Salesforce’s evolving focus on data protection, especially as AI adoption grows and data security becomes increasingly important. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Marketing Cloud Transactional Emails Salesforce Marketing Cloud Transactional Emails are immediate, automated, non-promotional messages crucial to business operations and customer satisfaction, such as order Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more

Read More
Healthcare IT and CrowdStrike

Healthcare IT and CrowdStrike

Learning from the CrowdStrike Outage: Enhancing Resilience and Incident Response Overview: In the wake of the CrowdStrike outage, businesses around the globe are focusing on restoring business continuity and bolstering their resilience for future incidents. On Friday, July 19, 2024, a faulty content update triggered crashes across approximately 8.5 million Windows devices, displaying the infamous blue screen of death. This affected a range of sectors, including hospitals and airlines. Although less than 1% of all Windows machines were impacted, the outage caused significant disruptions, particularly in healthcare. For instance, Mass General Brigham hospitals and clinics canceled all non-urgent visits on the day of the outage. Other major healthcare providers, such as Memorial Sloan Kettering Cancer Center, Cleveland Clinic, and Mount Sinai, also faced operational challenges. This incident was not a result of a cyberattack but rather a defective content configuration update to CrowdStrike’s Falcon threat detection platform. According to the company’s preliminary post-incident review, a bug in the content validator allowed the faulty update to pass through validation despite containing errors. “What we’re hearing is that the recovery is well underway. Most healthcare organizations I’ve been talking to are back up and running,” said David Finn, Executive Vice President of Governance, Risk, and Compliance at First Health Advisory, in an interview with TechTarget Editorial. “The scope was much smaller than some of the other issues we’ve seen in the recent past in healthcare, but the response was healthy. Still, I think there are a lot of lessons learned.” Health IT security experts suggest that this incident can serve as a valuable learning opportunity for improving future response and recovery strategies. Planning for the Inevitable “The bad thing is always going to happen,” Finn stated, drawing on his 40 years of experience in health IT security and privacy. “The trick is to plan for it, be prepared, and ensure your ability to recover and remain resilient.” Whether it’s a large-scale cyberattack, like the one at Change Healthcare in February 2024, or a global IT outage without malicious origins, healthcare organizations of all sizes must be ready to respond to a variety of incidents that could disrupt critical systems. Finn emphasized the importance of proactive due diligence and thorough incident response planning, particularly in identifying and addressing single points of failure. Preparing for potential operational challenges in advance can make all the difference when an incident actually occurs. “We have to change the way we think about deploying this stuff,” Finn added. “Software, fortunately or not, is written by human beings, and human beings will always make mistakes. It’s our job to protect against those kinds of mistakes.” The Importance of Resilience Cyber-resilience is essential for enabling organizations to quickly recover and restore operations. By understanding that incidents like the CrowdStrike outage are bound to occur, organizations can focus on building resilience to effectively manage such events. Finn highlighted the need for resilience and redundancy in response to incidents like the CrowdStrike outage. “I still trust CrowdStrike, but that trust doesn’t mean they’re going to be perfect every time,” Finn noted. Healthcare organizations responded quickly to the incident, despite the disruptions it caused. For instance, Mass General Brigham activated its incident command to manage its response, keeping clinics and emergency departments open for urgent cases. By Monday, July 22, they had resumed scheduled appointments and procedures. According to Erik Weinick, co-head of the privacy and cybersecurity practice at New York-based law firm Otterbourg, the CrowdStrike incident underscores the need for organizations to reassess their legal and technical risk protocols. “Although initial reports indicate that the incident was an accident, not an attack, organizations should use this incident as motivation to conduct information audits, penetration testing, update system mapping and software, including security patches, and remind users about best security practices like multifactor authentication and frequently changing difficult-to-guess passwords,” Weinick said. Essentially, organizations can leverage incidents like the CrowdStrike outage to strengthen their risk management strategies and enhance their cyber-resilience. Third-Party Risk Management Challenges Even with strict security controls in place, organizations are still vulnerable to risks from third-party vendors. As the interconnectedness of healthcare systems grows, so does the potential for third-party risks. The global IT outage highlighted the importance of third-party risk management and the associated challenges. In 2023 and 2022, some of the largest healthcare data breaches were caused by third-party vendors. “People probably did a lot of risk analysis around CrowdStrike, but I’ll bet no one ever asked what tools they use to produce their software,” Finn speculated. “Until we get standards in place for software development and certifications for software sold to critical infrastructure sectors, we’re going to have to dig a little deeper.” In response to the incident, CrowdStrike announced plans to enhance its software resilience and testing processes, including adding more validation checks to its Content Validator for Rapid Response Content to prevent the deployment of faulty content. The company also plans to conduct multiple independent third-party security code reviews to prevent similar incidents in the future. “On the legal front, organizations should review their vendor agreements to understand their obligations regarding privacy and data security, who their partners are working with, and what limitations exist on liability for incidents like the CrowdStrike outage,” Weinick advised. He also recommended checking business disruption insurance coverage and conducting tabletop exercises to rehearse business continuity and recovery procedures in the event of a systems outage. Key Takeaways The CrowdStrike outage reinforced essential IT and security considerations for organizations worldwide, particularly in the areas of resilience, third-party risk management, and incident response and recovery. By learning from this event, organizations can better prepare for future challenges and improve their overall cyber-resilience. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven
Read More
AI and Big Data

AI and Big Data

Over the past decade, enterprises have accumulated vast amounts of data, capturing everything from business processes to inventory statistics. This surge in data marked the onset of the big data revolution. However, merely storing and managing big data is no longer sufficient to extract its full value. As organizations become adept at handling big data, forward-thinking companies are now leveraging advanced analytics and the latest AI and machine learning techniques to unlock even greater insights. These technologies can identify patterns and provide cognitive capabilities across vast datasets, enabling organizations to elevate their data analytics to new levels. Additionally, the adoption of generative AI systems is on the rise, offering more conversational approaches to data analysis and enhancement. This allows organizations to extract significant insights from information that would otherwise remain untapped in data stores. How Are AI and Big Data Related? Applying machine learning algorithms to big data is a logical progression for companies aiming to maximize the potential of their data. Unlike traditional rules-based approaches that follow explicit instructions, machine learning systems use data-driven algorithms and statistical models to analyze and detect patterns in data. Big data serves as the raw material for these systems, which derive valuable insights from it. Organizations are increasingly recognizing the benefits of integrating big data with machine learning. However, to fully harness the power of both, it’s crucial to understand their individual capabilities. Understanding Big Data Big data involves extracting and analyzing information from large quantities of data, but volume is just one aspect. Other critical “Vs” of big data that enterprises must manage include velocity, variety, veracity, validity, visualization, and value. Understanding Machine Learning Machine learning, the backbone of modern AI, adds significant value to big data applications by deriving deeper insights. These systems learn and adapt over time without the need for explicit programming, using statistical models to analyze and infer patterns from data. Historically, companies relied on complex, rules-based systems for reporting, which often proved inflexible and unable to cope with constant changes. Today, machine learning and deep learning enable systems to learn from big data, enhancing decision-making, business intelligence, and predictive analysis. The strength of machine learning lies in its ability to discover patterns in data. The more data available, the more these algorithms can identify patterns and apply them to future data. Applications range from recommendation systems and anomaly detection to image recognition and natural language processing (NLP). Categories of Machine Learning Algorithms Machine learning algorithms generally fall into three categories: The most powerful large language models (LLMs), which underpin today’s widely used generative AI systems, utilize a combination of these methods, learning from massive datasets. Understanding Generative AI Generative AI models are among the most powerful and popular AI applications, creating new data based on patterns learned from extensive training datasets. These models, which interact with users through conversational interfaces, are trained on vast amounts of internet data, including conversations, interviews, and social media posts. With pre-trained LLMs, users can generate new text, images, audio, and other outputs using natural language prompts, without the need for coding or specialized models. How Does AI Benefit Big Data? AI, combined with big data, is transforming businesses across various sectors. Key benefits include: Big Data and Machine Learning: A Synergistic Relationship Big data and machine learning are not competing concepts; when combined, they deliver remarkable results. Emerging big data techniques offer powerful ways to manage and analyze data, while machine learning models extract valuable insights from it. Successfully handling the various “Vs” of big data enhances the accuracy and power of machine learning models, leading to better business outcomes. The volume of data is expected to grow exponentially, with predictions of over 660 zettabytes of data worldwide by 2030. As data continues to amass, machine learning will become increasingly reliant on big data, and companies that fail to leverage this combination will struggle to keep up. Examples of AI and Big Data in Action Many organizations are already harnessing the power of machine learning-enhanced big data analytics: Conclusion The integration of AI and big data is crucial for organizations seeking to drive digital transformation and gain a competitive edge. As companies continue to combine these technologies, they will unlock new opportunities for personalization, efficiency, and innovation, ensuring they remain at the forefront of their industries. Like Related Posts Who is Salesforce? Who is Salesforce? Here is their story in their own words. From our inception, we’ve proudly embraced the identity of Read more Salesforce Marketing Cloud Transactional Emails Salesforce Marketing Cloud Transactional Emails are immediate, automated, non-promotional messages crucial to business operations and customer satisfaction, such as order Read more Salesforce Unites Einstein Analytics with Financial CRM Salesforce has unveiled a comprehensive analytics solution tailored for wealth managers, home office professionals, and retail bankers, merging its Financial Read more AI-Driven Propensity Scores AI plays a crucial role in propensity score estimation as it can discern underlying patterns between treatments and confounding variables Read more
Read More
gettectonic.com